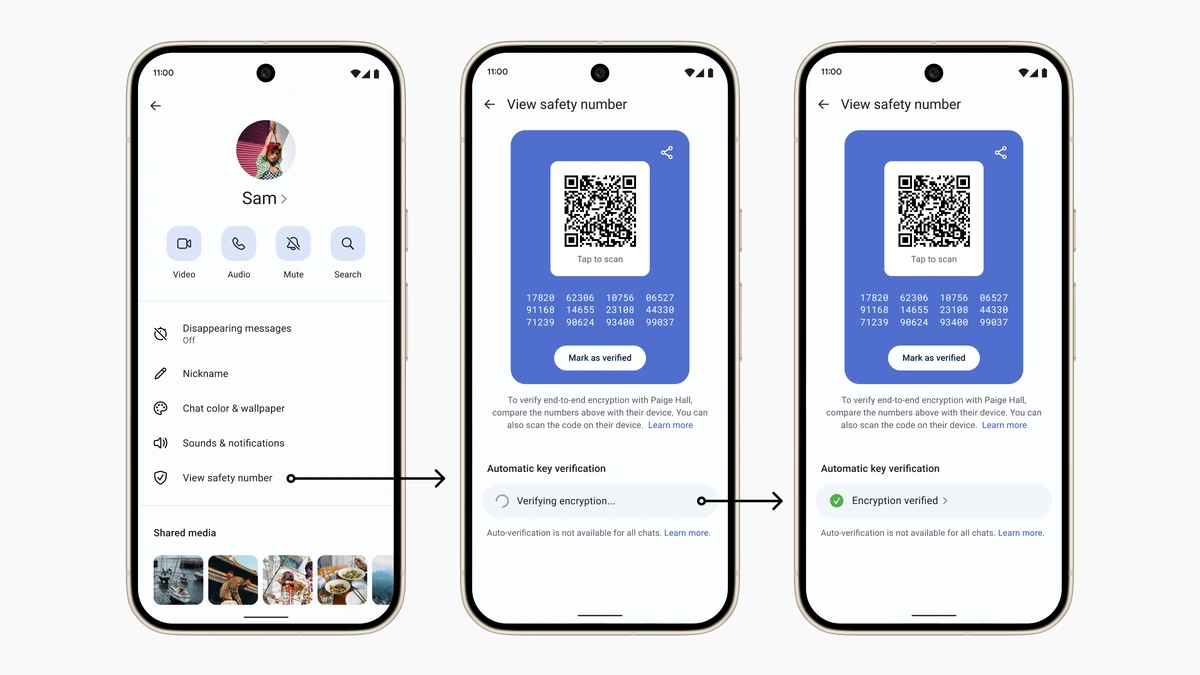
Signal added automatic key verification, a cryptographic protection layer that lets users confirm they are communicating with the right person without an in-person meeting or a secondary trusted channel.
The feature addresses a structural limitation of centralized key directories. Signal's end-to-end encrypted messaging depends on each device fetching the correct public encryption key for its recipient from a central directory. If that directory were compromised by an outsider bypassing cloud-provider security, or by a privileged insider deliberately targeting a specific account, an attacker could substitute a different key and read or alter messages in transit, a scenario Signal describes as a "Mallory in the middle" attack. The existing safety number system guards against this, but requires either an in-person QR code scan or comparison via a secondary trusted channel.
Automatic key verification removes that dependency through three coordinated mechanisms. A log tree records every key registration and change in an append-only structure. A set of prefix trees provides an efficient binary-search path through the log so the app can verify any given key without scanning the entire history. Cloudflare and Trail of Bits serve as independent third-party auditors, each signing new log entries to prevent Signal from quietly presenting different views of the key directory to different users. All public identifiers are cryptographically obscured, processed through a verifiable random function, so auditors never see plaintext user data. The full architecture is documented in Signal's key transparency technical overview, which also links to an open-source implementation derived from an IETF key transparency protocol draft.
In the Signal app, the feature appears under "View Safety Number" in a contact's profile. Tapping "Verify automatically" displays a green checkmark and "Encryption verified" when verification succeeds. Signal automatically monitors its own users' key data in the log on a regular cadence; checking a contact's key requires a user-initiated tap. One current constraint: automatic key verification requires your device to have the contact's phone number. Connections established via username alone, without a phone number exchange, cannot be automatically verified until a phone number is shared.
Signal scopes the guarantee precisely. Key transparency confirms that all devices in Signal's ecosystem share the same view of the association between a phone number or username and its encryption key, not the identity of the person who controls that account. A full account takeover, as distinct from a directory-level key substitution, would still require the manual safety number process to detect. Users who prefer to avoid reliance on any third-party auditor can disable automatic key verification under "Privacy" > "Advanced" > "Automatic Key Verification."