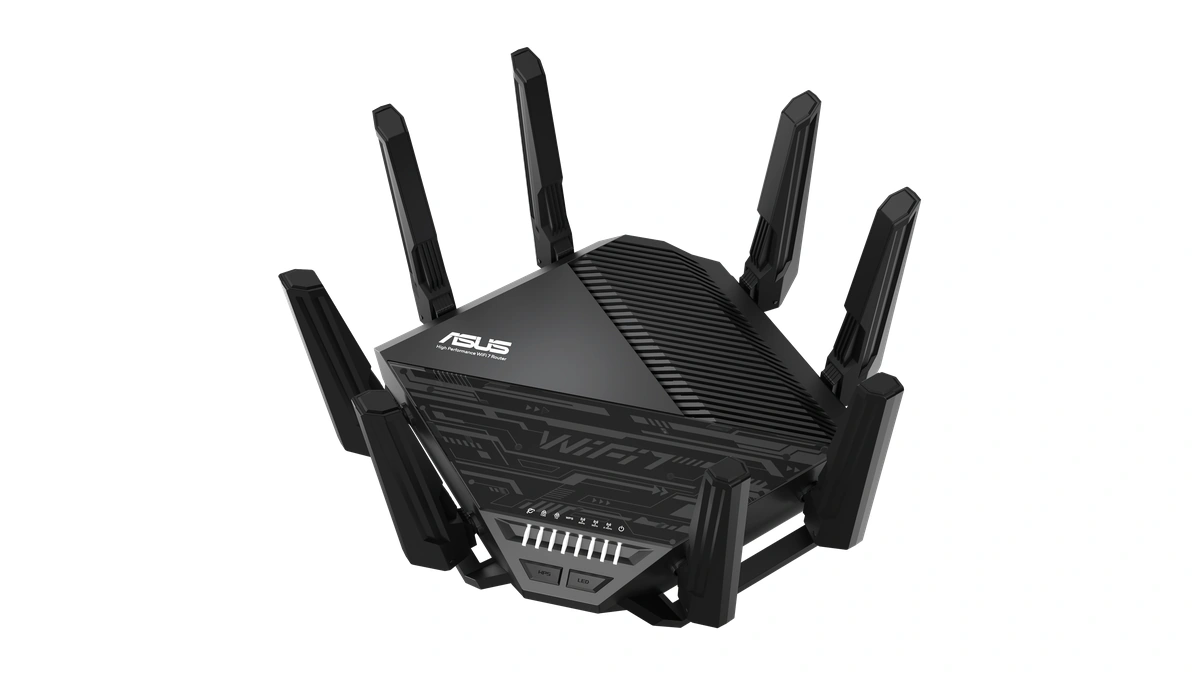
ASUS has patched two router firmware flaws that let a logged-in attacker run commands on the device, one of them through a crafted VPN configuration file.
ASUS lists the VPN-file flaw as CVE-2026-14157 and scores it 9.4 (Critical) on the CVSS 4.0 scale. The company says the bug sits in the web management interface of routers running the 3.0.0.6_102 firmware series, where an authenticated remote attacker could upload a crafted VPN client configuration file and execute arbitrary commands on the device. Until the update is installed, ASUS tells owners to import VPN client configuration files only from trusted sources. It also says to avoid any file that was shared publicly, came from an unknown source or cannot be verified as trustworthy.
The second bulletin covers CVE-2026-13313, rated 8.9 (High). ASUS says a remote authenticated attacker could execute commands with elevated privileges on routers in the 3.0.0.4_386, 3.0.0.4_388 and 3.0.0.6_102 series. The bulletin gives no entry point beyond that. Its mitigation advice does hint at one: ASUS warns that attackers may use social engineering to trick administrators into running crafted commands that interact with the router's administration interface. Scripts and tools from untrusted sources, it says, should stay off every device on the local network.
Both bulletins describe an authenticated attacker, and the CVSS vectors ASUS publishes rate the privileges required as high for each flaw. That puts the administration login at the center of the risk. A weak or reused admin password would give an attacker the entry either bug needs. ASUS's guidance with the second bulletin points the same way: administrator passwords of at least 10 characters that mix upper-case letters, numbers and symbols, plus strong, unique router login and Wi-Fi passwords on end-of-life models that will not receive new firmware.
Neither bulletin names router models, only firmware series, and neither says whether the flaws are being exploited. Owners will have to match the firmware version their router reports against those series. ASUS urges all users to take the latest build from its Support page immediately.